
OpenVPN for every client. One panel.
TunnelDesk runs your OpenVPN server from the browser and puts AI on top of it: it spots sign-ins that do not look like the user, explains why a connection failed, and suggests the access each group really needs. Users, certificates, firewall-enforced access lists, branch exits and a DNS filter — in one Go binary with SQLite.
A synthetic MSP with 120 VPN users across four client companies, running live on the server.
See it running, in under two minutes
Narrated tours of the product on the same synthetic data. The live application itself is shown on a call.
Based on AI. Built for AI.
AI runs inside the product, and the product is ready for the AI agents your team already uses.
AI at the core, not bolted on
- Sign-ins that do not look right: a new country, a new device or an odd hour for that user is scored and flagged before it becomes an incident.
- "Why can't I connect?" answered: the AI reads the server log and tells your helpdesk the cause and the fix in one sentence.
- Least privilege from real use: access lists suggested per group from the traffic people actually send, ready to apply.
- A morning brief: who connected, what was blocked and what changed overnight, written for a human.
Ready for your AI agents
- An MCP server built in: Claude, ChatGPT, Copilot or your own agent can add a user, revoke a certificate or ask who is connected — with exactly the rights of the user who connected it.
- An API written for agents: every endpoint described in OpenAPI, scoped keys per area, and answers in plain JSON a model can read.
- Guardrails on every action: Every action an agent takes is checked against the user's group rights and written to the audit log.
- Your data stays yours: self-hosted, with the model of your choice — cloud or local — and nothing sent to train anyone else's.
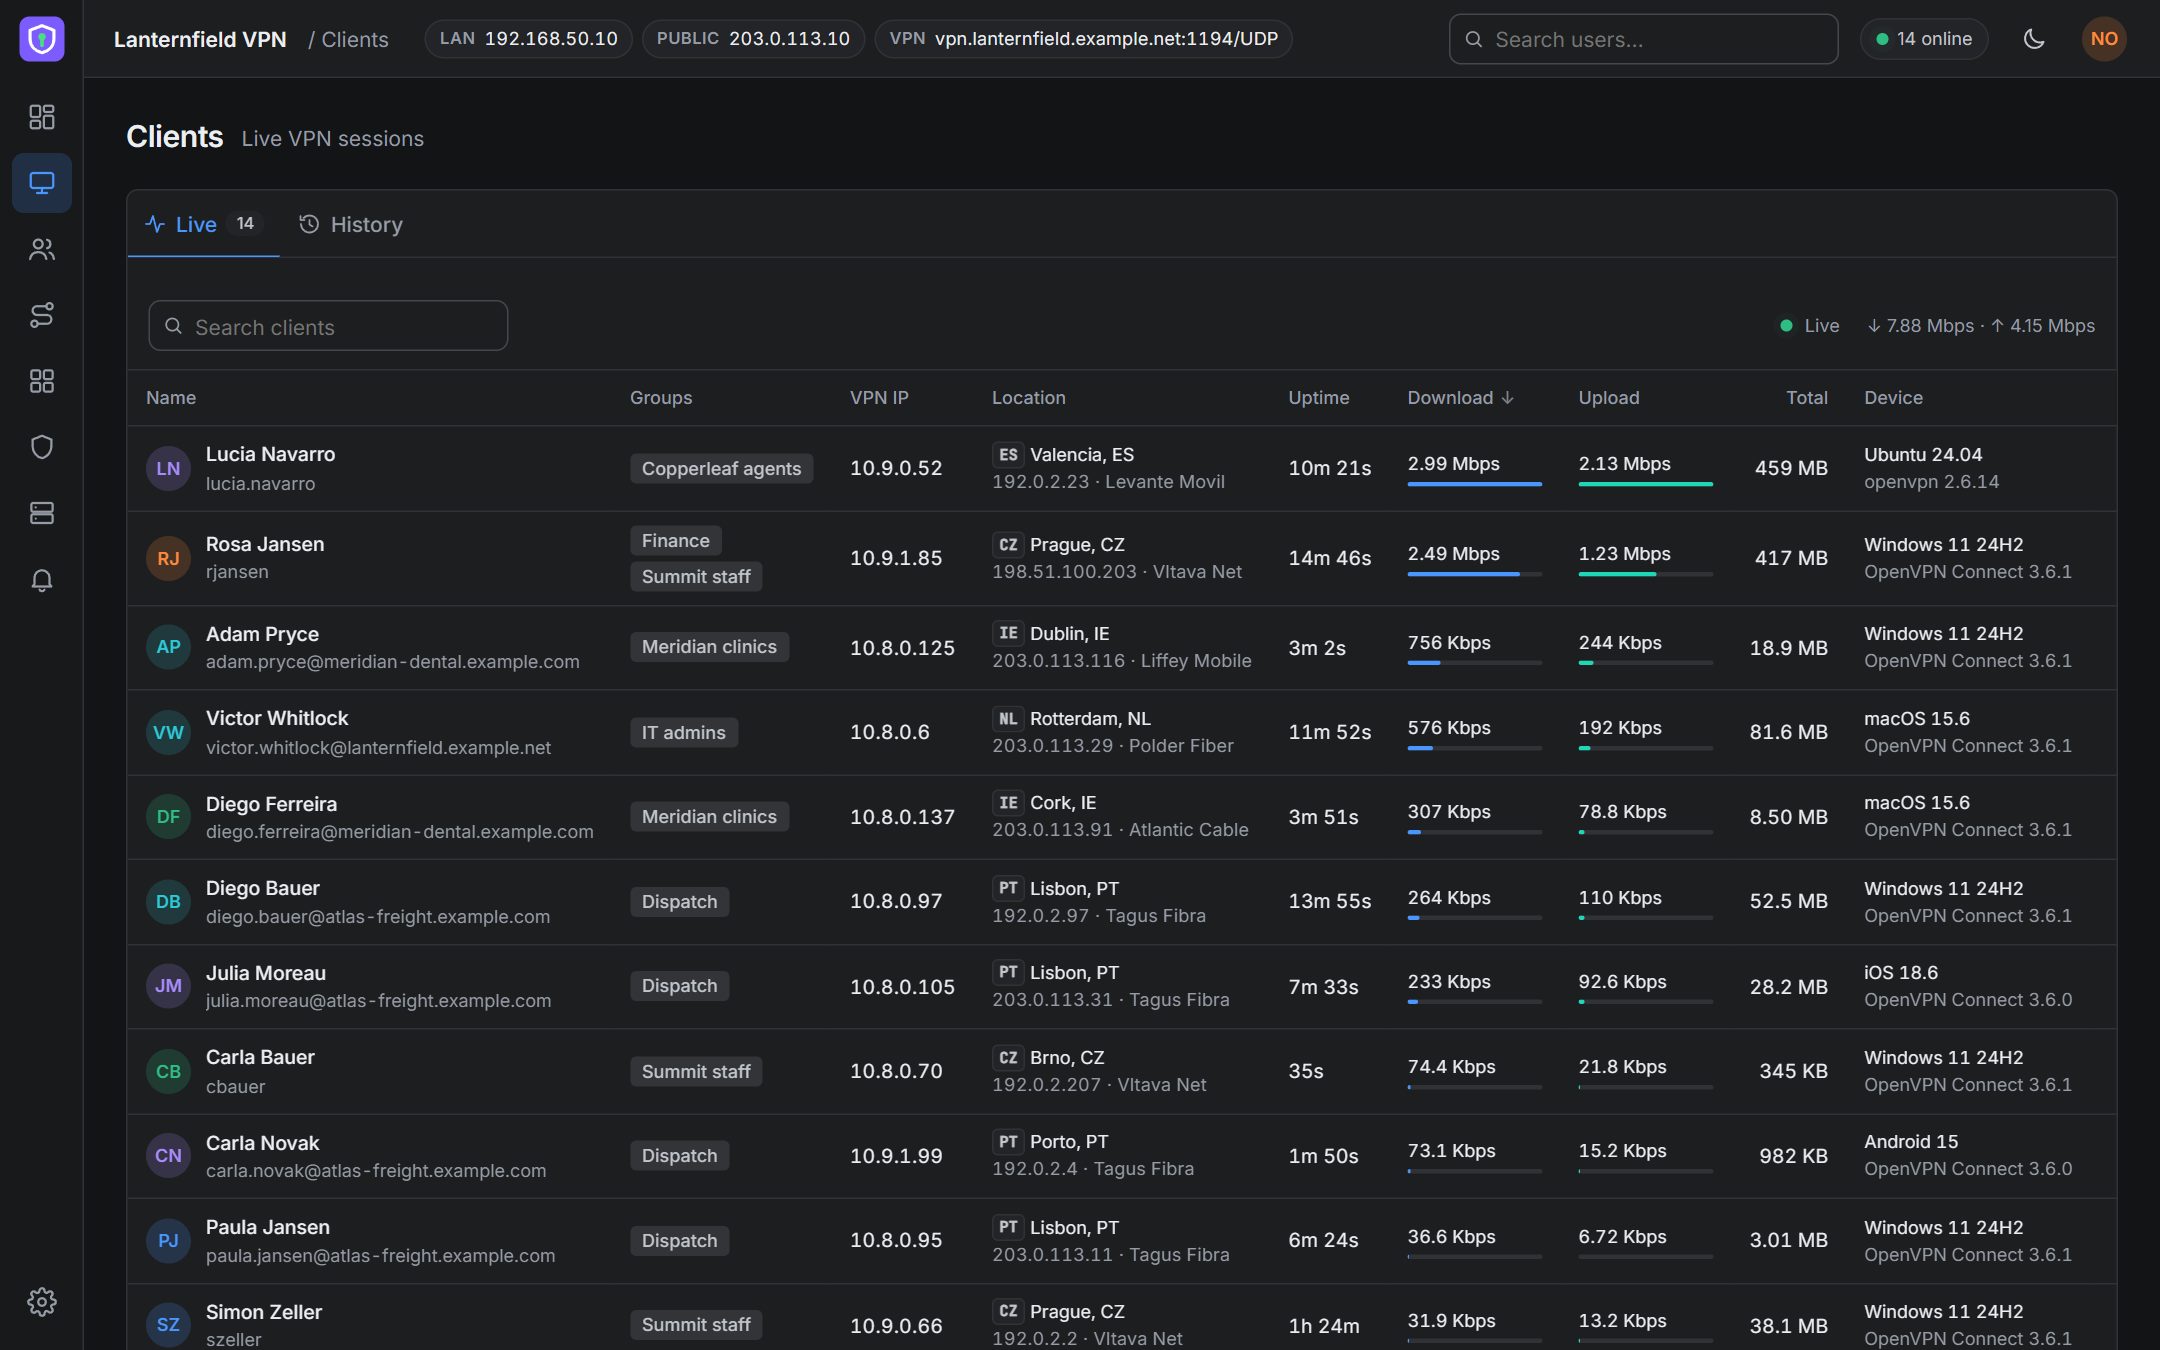
Who is connected, from where, and how fast
- 1Every session in real time: throughput read from OpenVPN’s management interface, VPN and public address, uptime and bytes.
- 2Location, network and device: for each connection — “Windows 11, OpenVPN Connect, from a hotel in Paris” instead of a bare IP.
- 3Disconnect in one click: or open the user: certificate, groups, what they can reach and their last sessions.
- A dashboard per admin: drag, resize and pick widgets — top apps, blocked lookups, health, recent sessions.
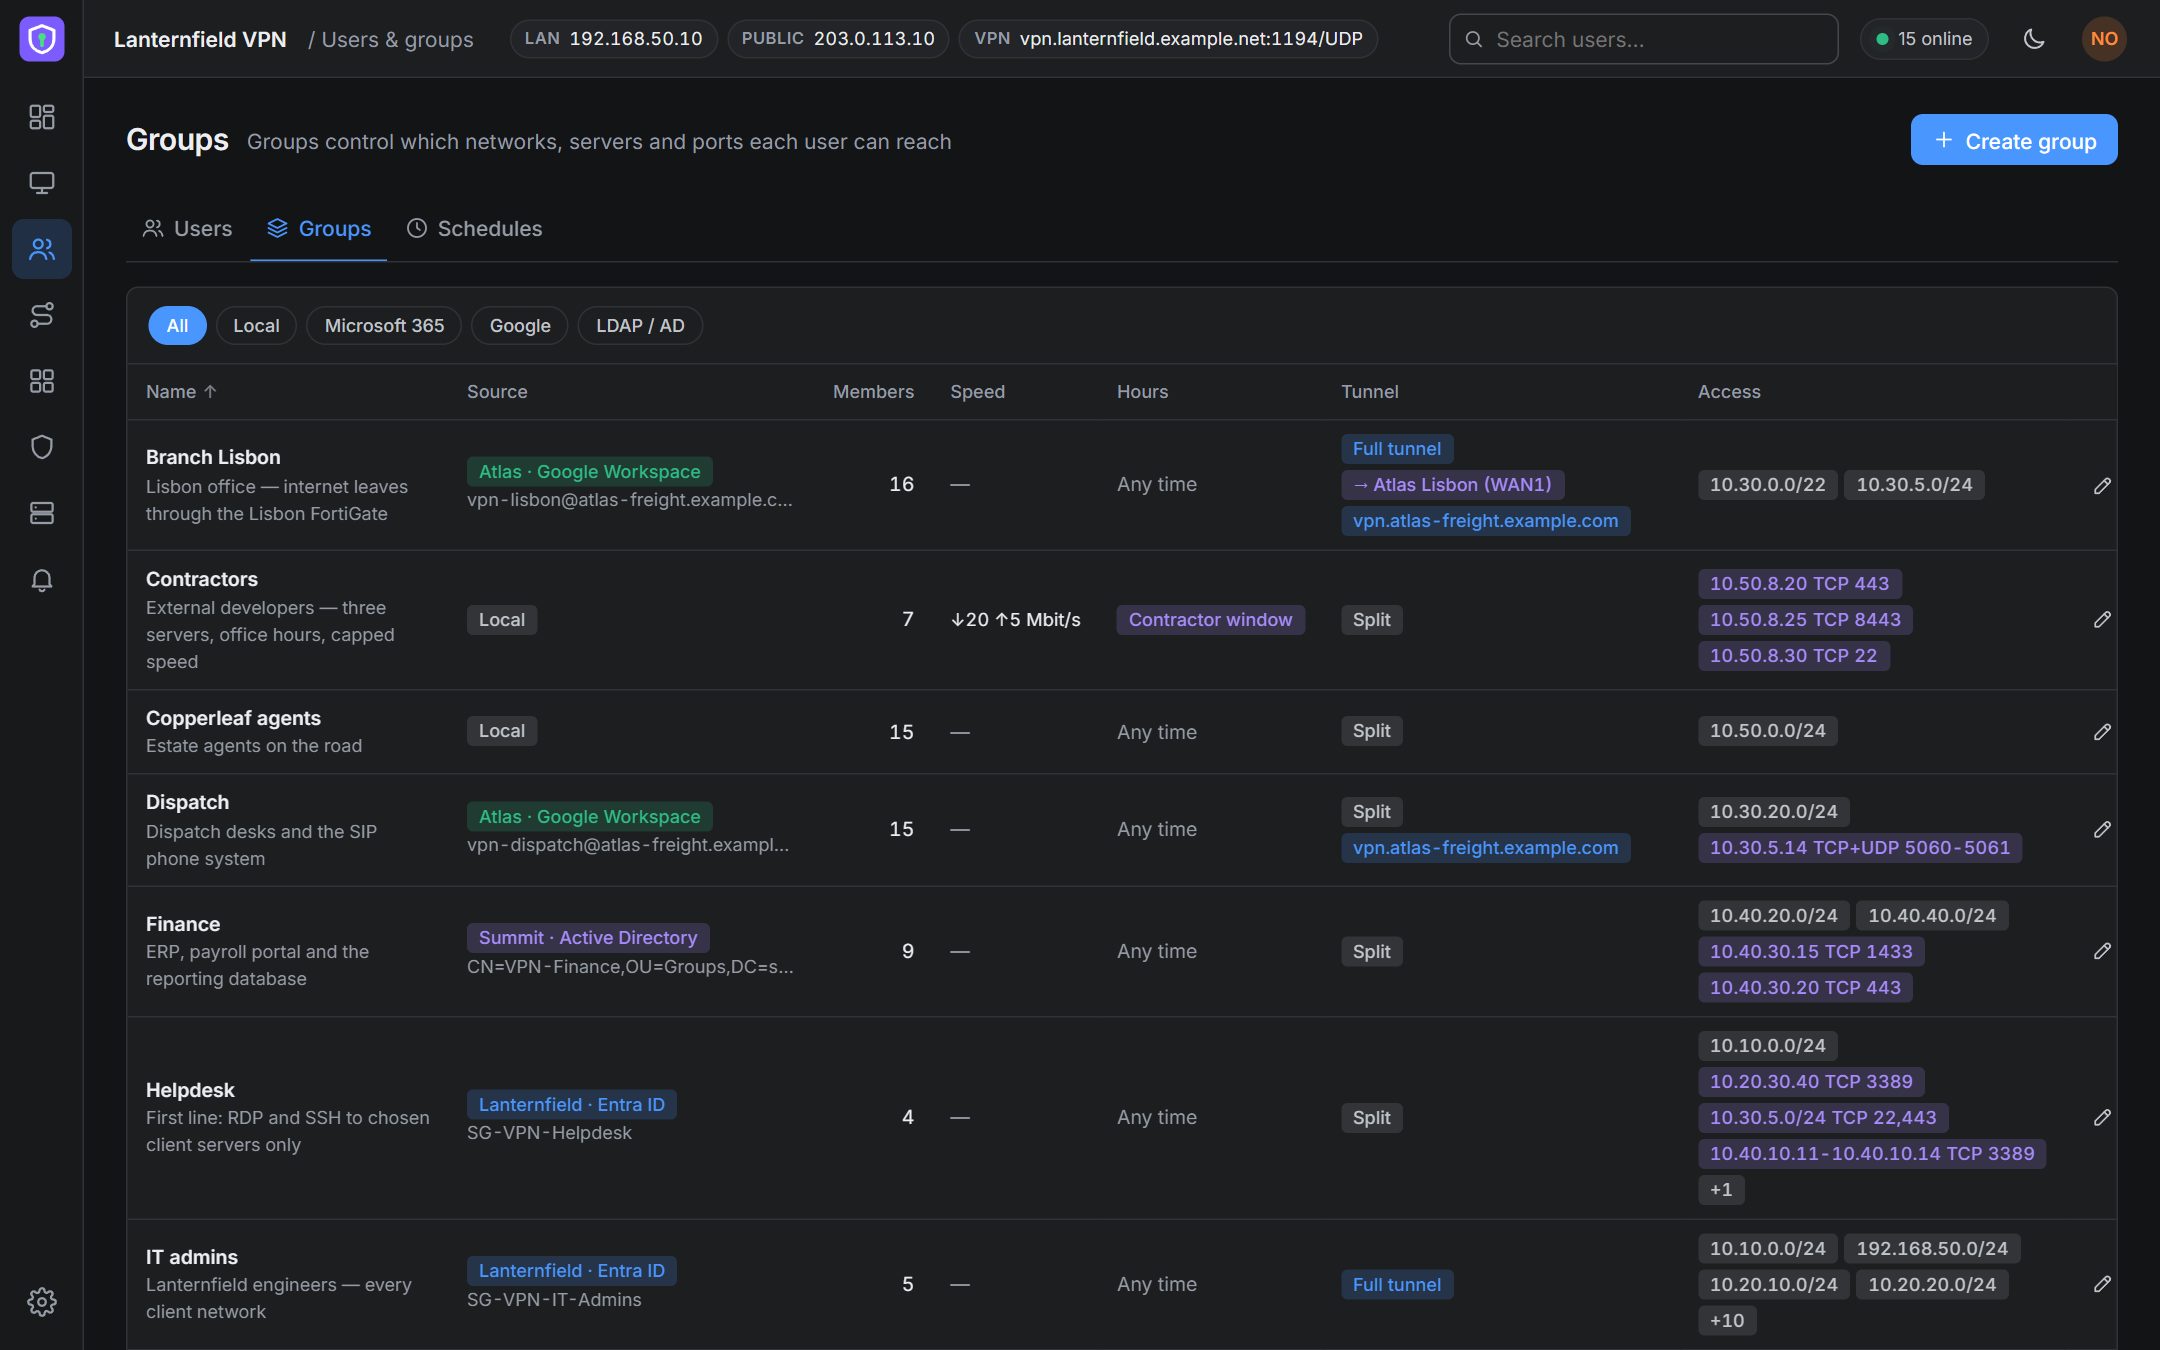
Each user reaches exactly what their group allows
- 1Groups set the networks: their members get — or full tunnel — and the tunnel mode switches with one click; the device reconnects by itself.
- 2Access entries down to a port: 10.20.30.40 TCP 3389 gives the helpdesk RDP to one server and nothing else. Enforced in the server’s firewall, not just in pushed routes.
- Certificates handled: issue, revoke, reissue, warnings before they expire. Profiles as an .ovpn download or a share link that dies after three downloads.
- 4Microsoft 365, Google Workspace, Active Directory: users sync from mapped groups and sign in to the VPN with MFA in the browser.
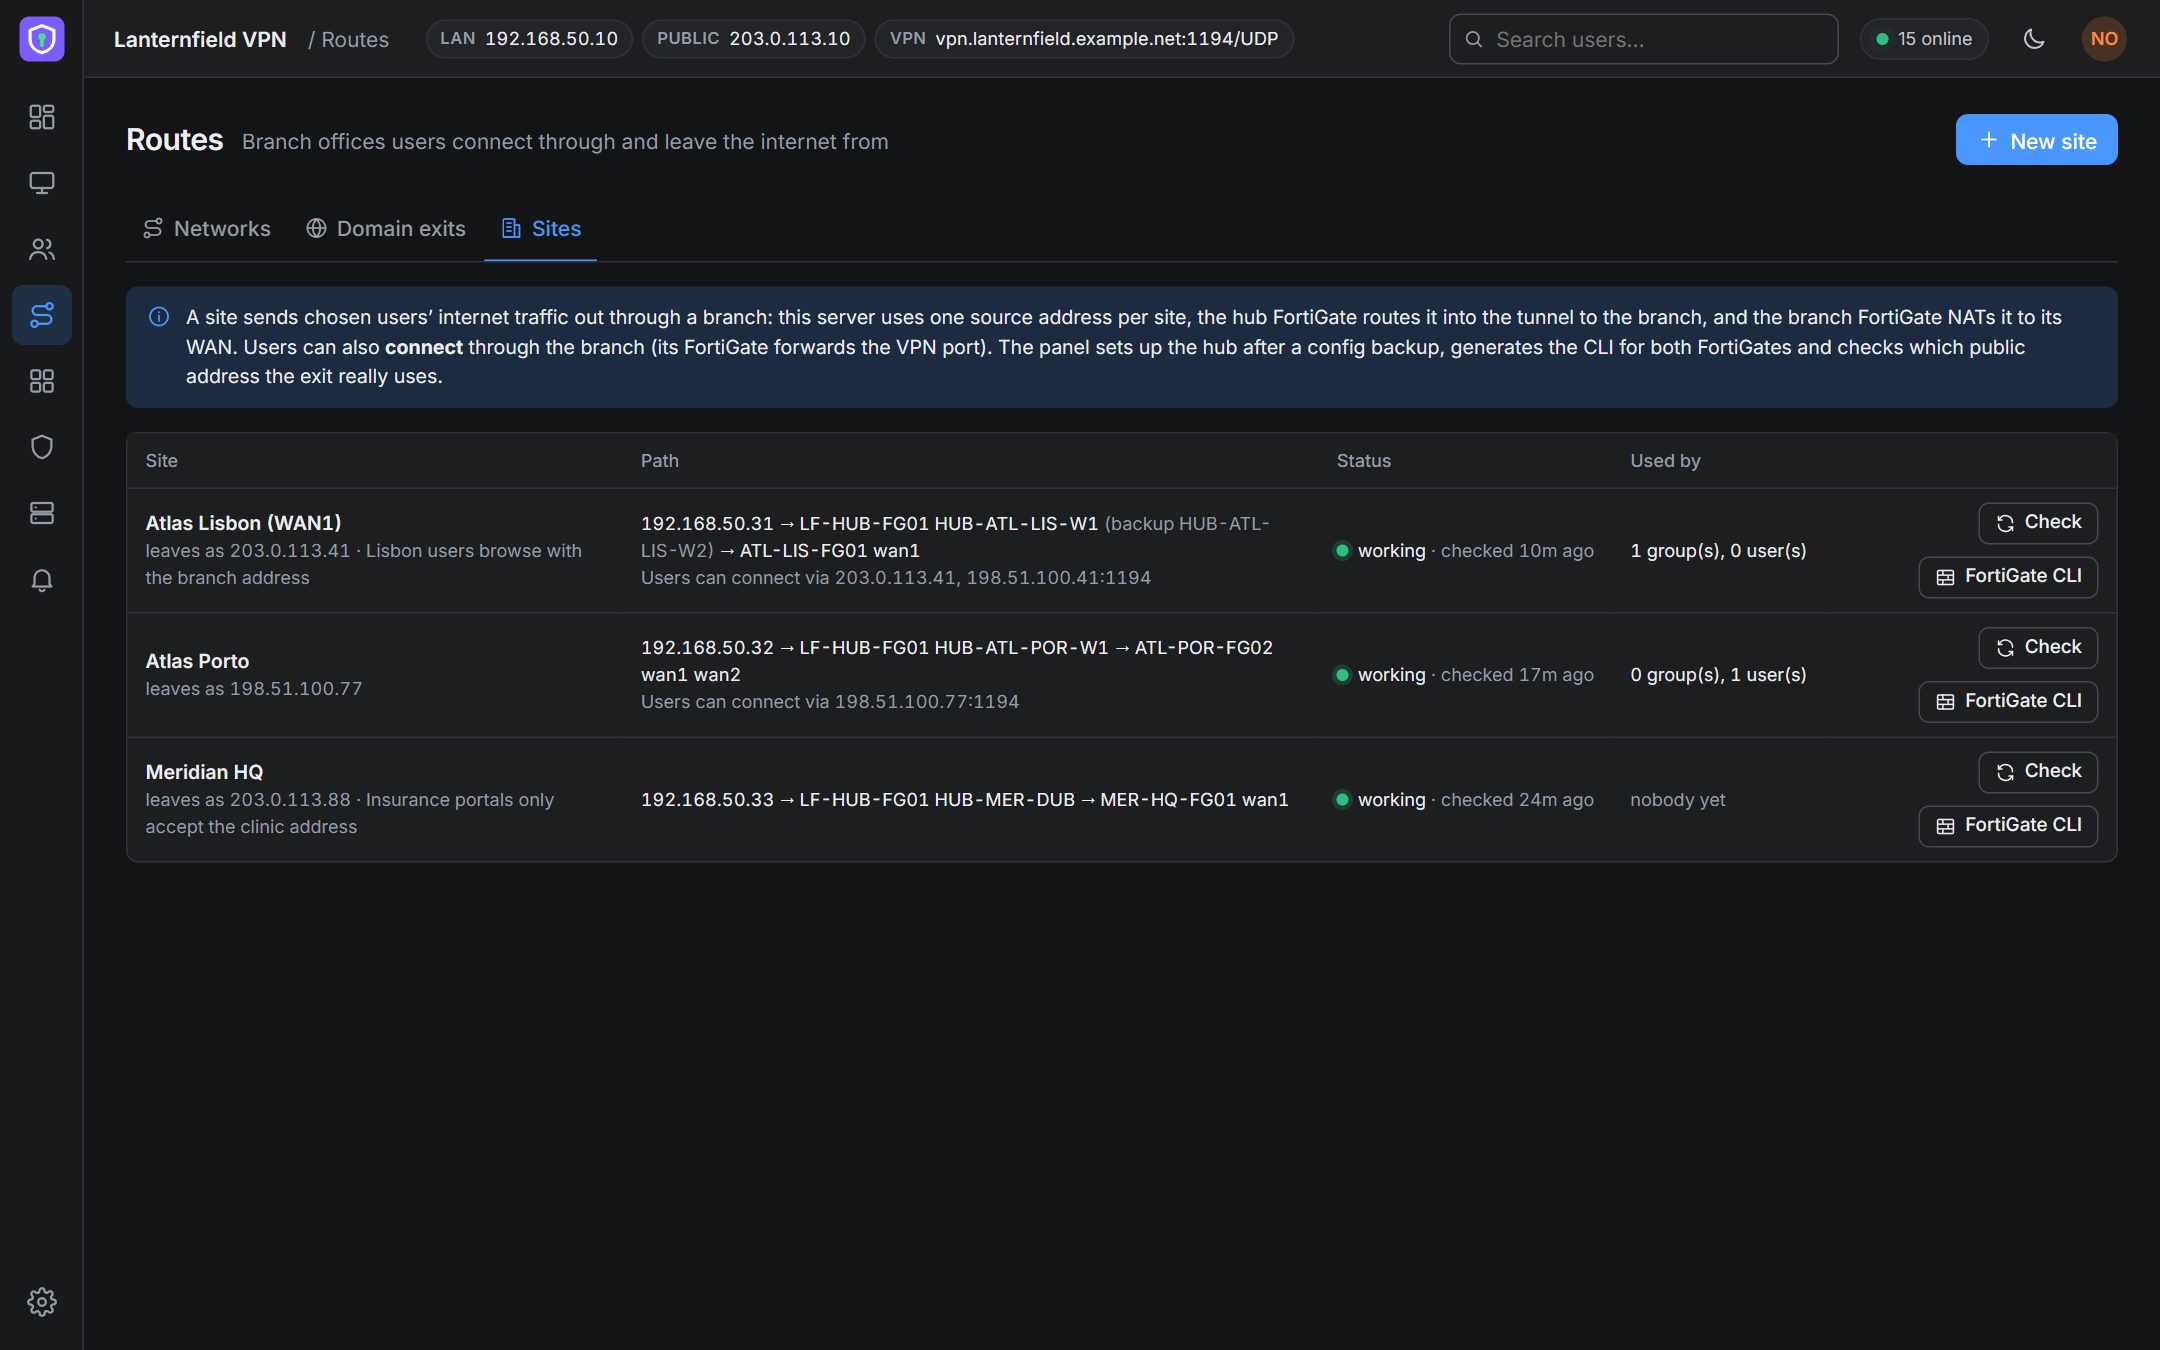
Out to the internet through the right office
- FortiGate networks discovered: when you add one and every six hours — import them as routes for chosen groups.
- 2Internet exit per group or user: the Lisbon team browses with the Lisbon branch’s public address, through its FortiGate.
- Domain exits: send only the insurance portal through the clinic’s line, learned live by the panel’s DNS resolver.
- 4CLI for both FortiGates: the hub configured after a config backup, and a check of the address the exit really uses.
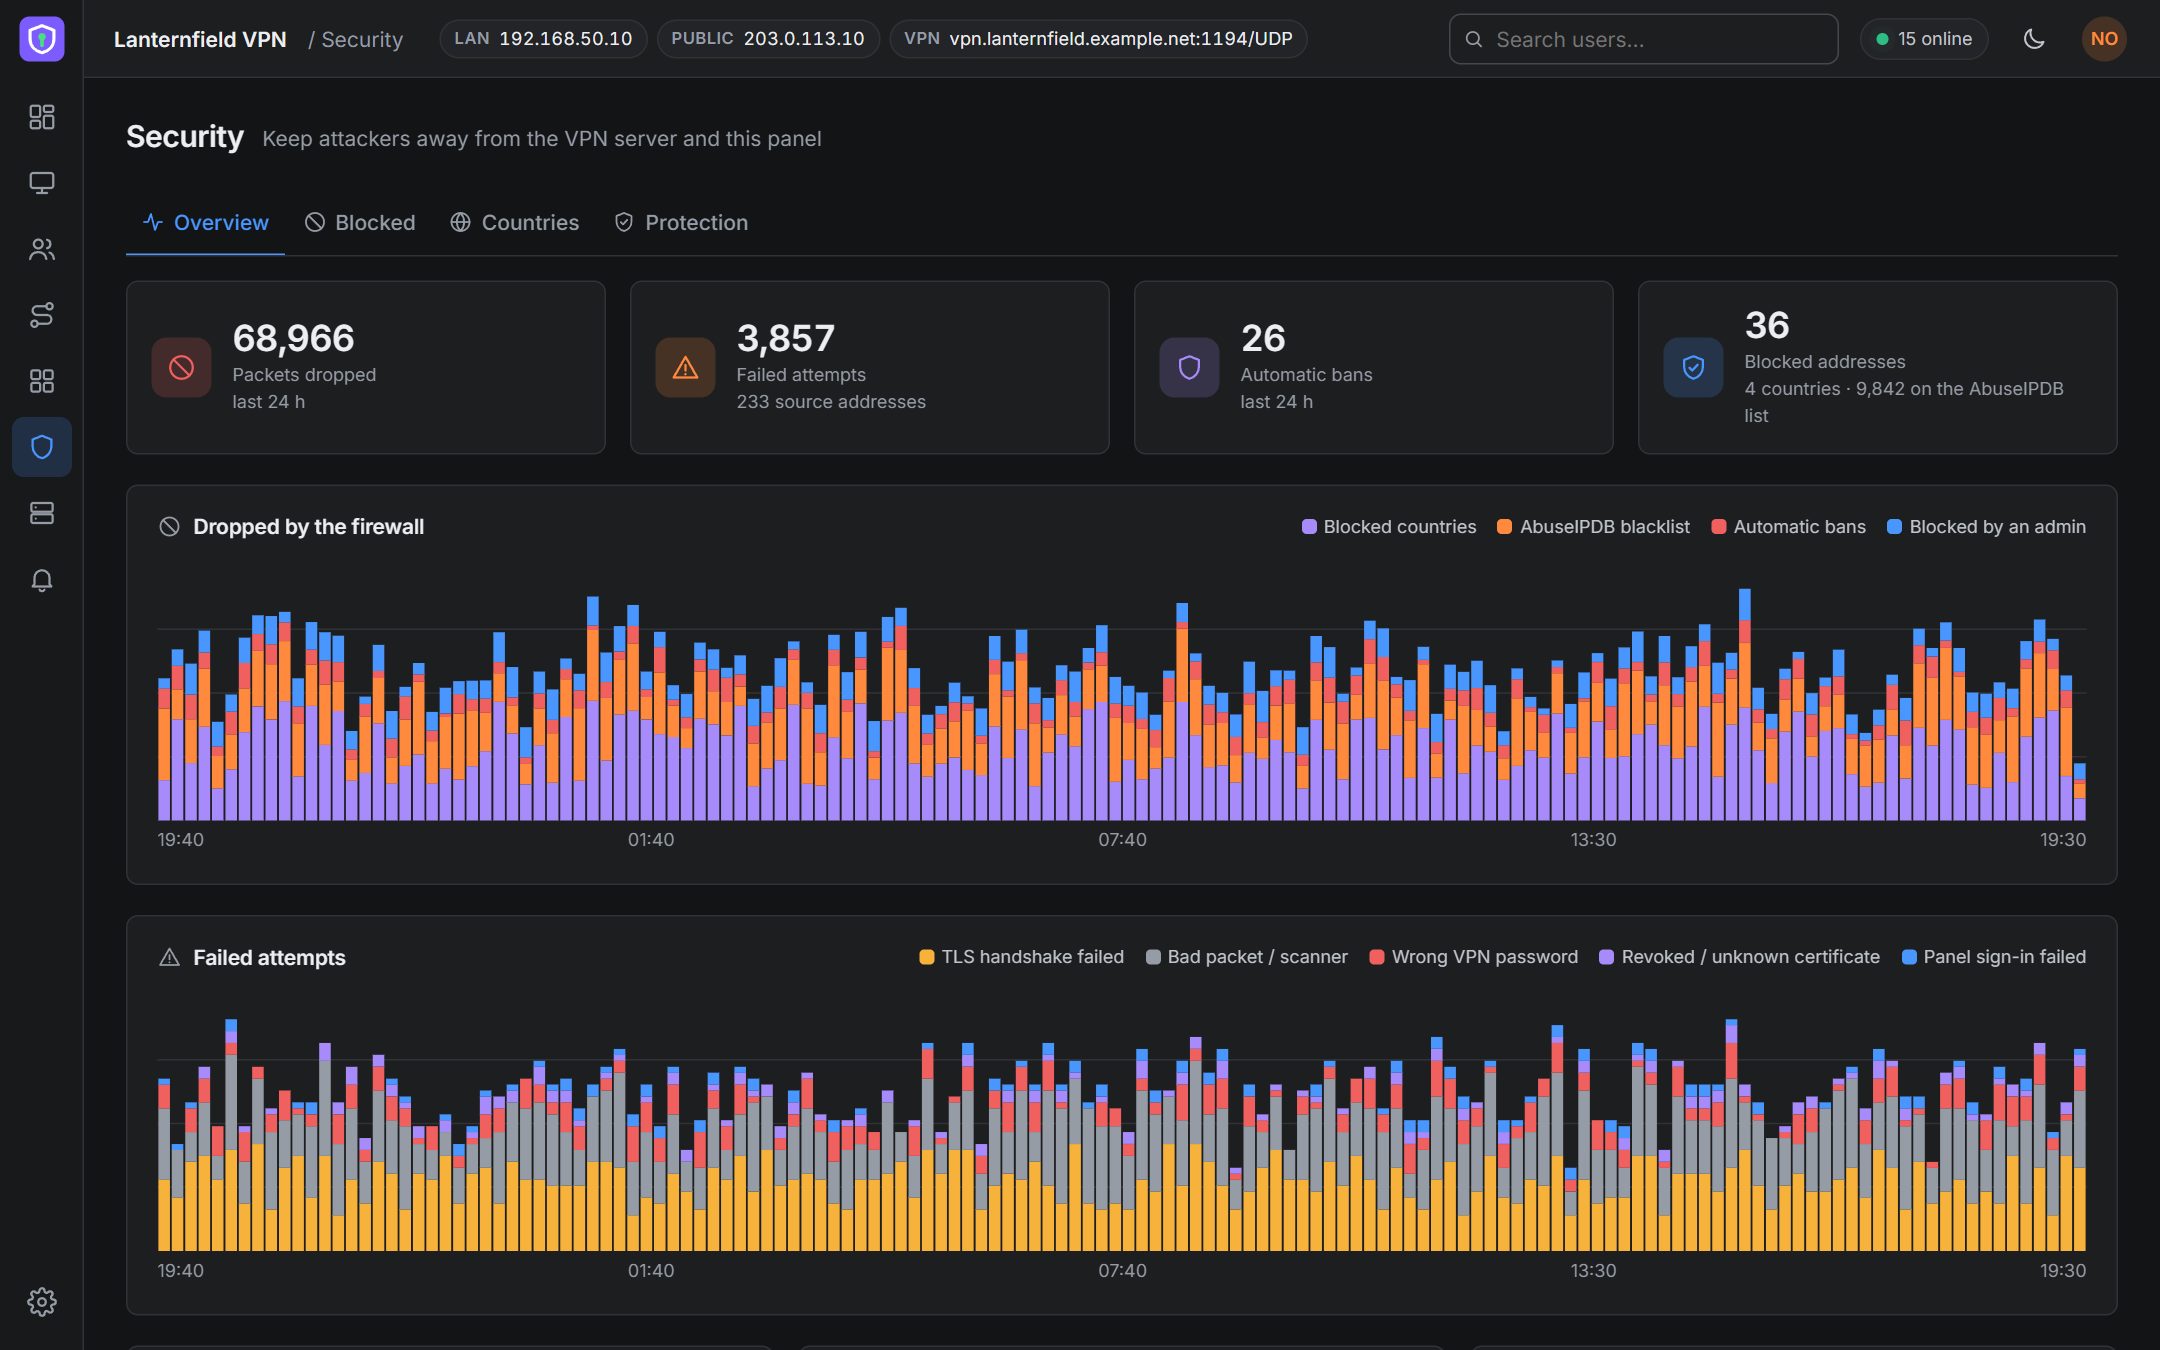
Scanners stay out. Users stay on track.
- 1Automatic bans: for sources that keep failing — TLS handshakes, wrong passwords, panel sign-ins — plus country blocks and the AbuseIPDB blacklist.
- A DNS filter on the tunnel: maintained blocklists, rules per group (no torrents, no social media for contractors) and a block page with access requests.
- Apps & traffic per user: which apps and sites each person reaches, kept 90 days.
- Alerts to Telegram and Slack: per event: connects with location, failed sign-ins, expiring certificates, backups, a daily digest.
The panel decides every connection
OpenVPN asks the panel about each client: the certificate must belong to an enabled user, the second factor must match their directory, and only their groups’ routes are pushed. If the panel is down, connected clients stay up.
Second factor per directory
Local users get a generated password; Microsoft and Google users sign in in the browser with MFA; Active Directory users bind with their own password.
Access lists in the firewall
Rebuilt atomically on every connect and change. Full-tunnel users still browse; everything internal they were not given is rejected.
Profiles people can use
A setup guide with download links for every platform, the profile by email or Telegram, and a self-service sign-up page for your directories.
Encrypted backups
Daily AES-256 archives to the server, Telegram, S3 or FTP with 14-day retention — and a restore from the panel, part by part.
More servers in one click
Deploy and harden a fresh VPS as a VPN node with the same users and certificates, or as an independent panel for a client.
Insights every morning
Unstable connections, failed handshakes, users who never connected, expiring certificates — with the log lines behind each one.
Built for people who run VPN for others
MSPs with many clients
Groups and directories per client company, and a VPN address per customer — vpn.customer-a.example.com — written into their profiles.
IT teams with branch offices
Users connect through their nearest branch and leave through it; the panel talks to the FortiGates so nobody types CLI on a Friday night.
Anyone tired of openvpn-ui
The panel owns server.conf and the firewall rules and regenerates them from Settings, keeping the previous config as a backup.
Auditors and owners
An audit log of every admin action, read-only admin accounts, an admin IP allow-list and HTTPS by default.
Your helpdesk
Search a user, see their last sessions and device, reissue a certificate and send a fresh profile — in under a minute.
Self-hosted
Runs next to OpenVPN on one small Linux VM. Your certificates and keys never leave your server.
Tell us what you're trying to achieve.
Book a 30-minute call or send a message and you'll reach a senior RHC Solutions consultant — not a ticket queue. Tell us how many VPN users and client companies you run, and which directories and firewalls are involved, and we'll come back with a walkthrough on a setup like yours within one business day.
Everything shown in this demo is synthetic: every company, person, number and address is invented. OpenVPN is a trademark of OpenVPN Inc.; FortiGate is a trademark of Fortinet, Inc.; UniFi is a trademark of Ubiquiti Inc. TunnelDesk is not affiliated with any of them.